Free book
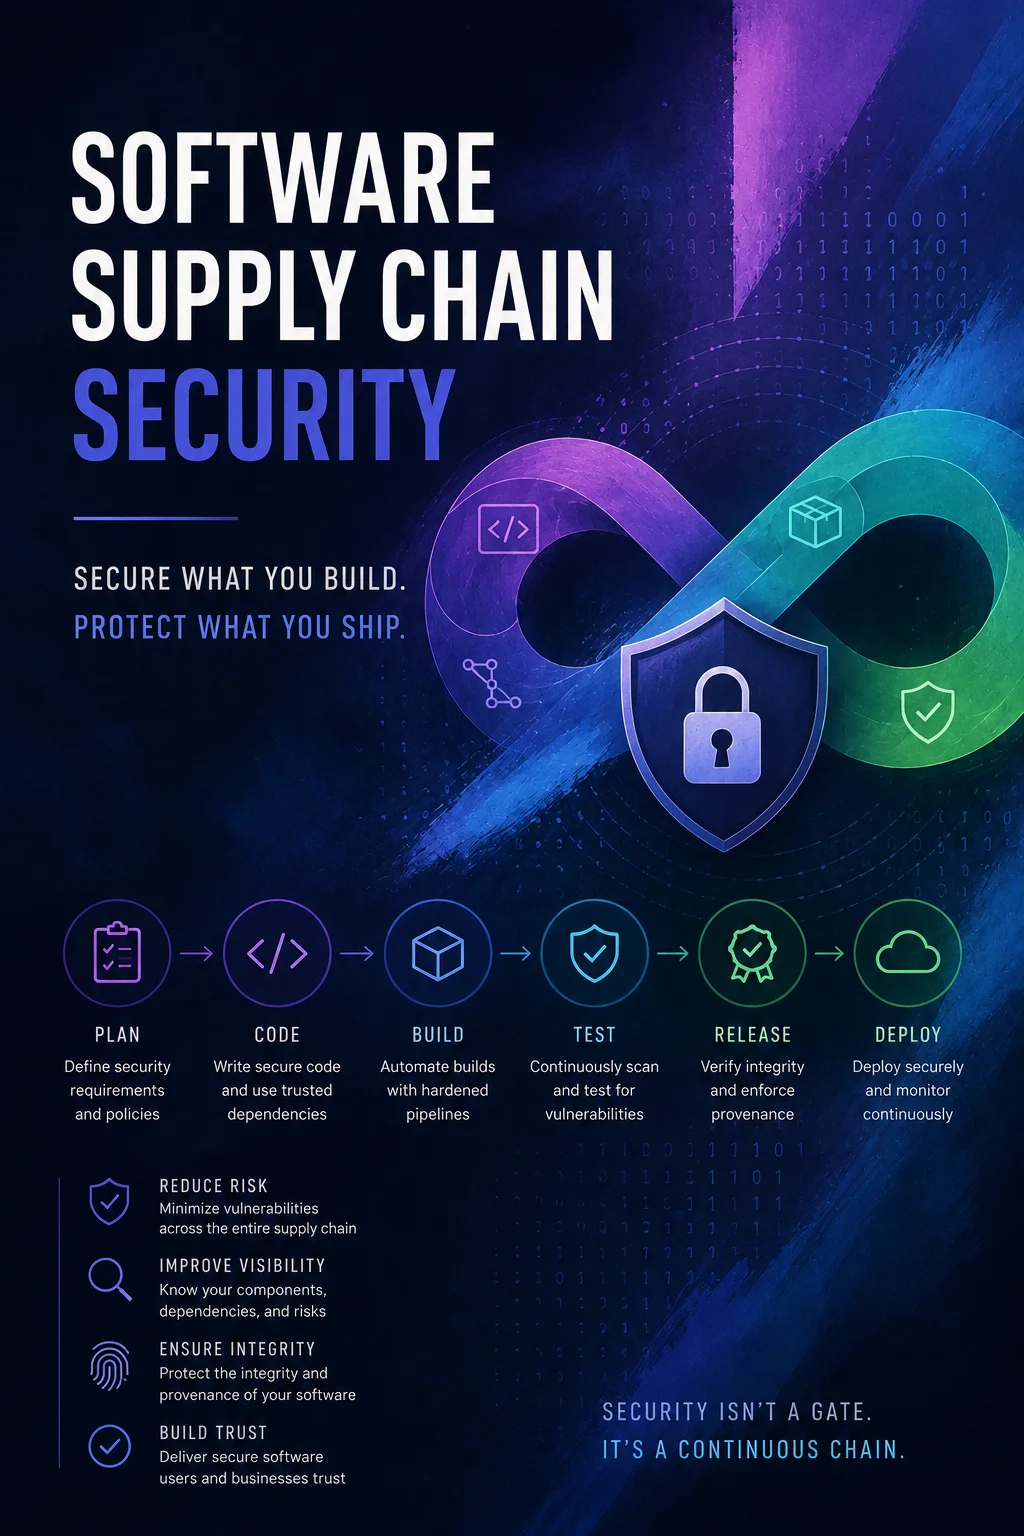
Software Supply Chain Security
Reading access
Free book
A modern software supply chain security book covering dependency risk, SBOMs, provenance, signed artifacts, SLSA concepts, CI/CD hardening, secrets, package registries, and release integrity.
Level: advancedLanguage: EN EnglishRating: 0Reviews: 0
Book
Book contents
01Chapter 1: How Software Supply Chains Are Attacked02Chapter 2: Dependencies, Registries, and Package Trust03Chapter 3: Build Systems, CI Runners, and Release Risk04Chapter 4: Threat Modeling the Delivery Pipeline05Chapter 5: Lockfiles, Pinning, and Dependency Review06Chapter 6: SBOMs and Vulnerability Management07Chapter 7: Artifact Signing and Provenance08Chapter 8: Secrets Management in CI/CD09Chapter 9: SLSA Concepts and Practical Adoption10Chapter 10: Container Image Security and Scanning11Chapter 11: Policy Gates and Release Approvals12Chapter 12: Incident Response for Compromised Dependencies13Chapter 13: Harden a Node.js Release Pipeline14Chapter 14: Add SBOM and Artifact Signing15Chapter 15: Create a Dependency Upgrade Workflow16Chapter 16: Build a Supply Chain Security Checklist17Appendix E: Deeper Practice and Extra Examples
Reviews
No approved reviews are visible yet.
Featured Books
Discussion
0 commentsNo approved comments are visible yet. New community replies may wait for moderation.