كتاب مجاني
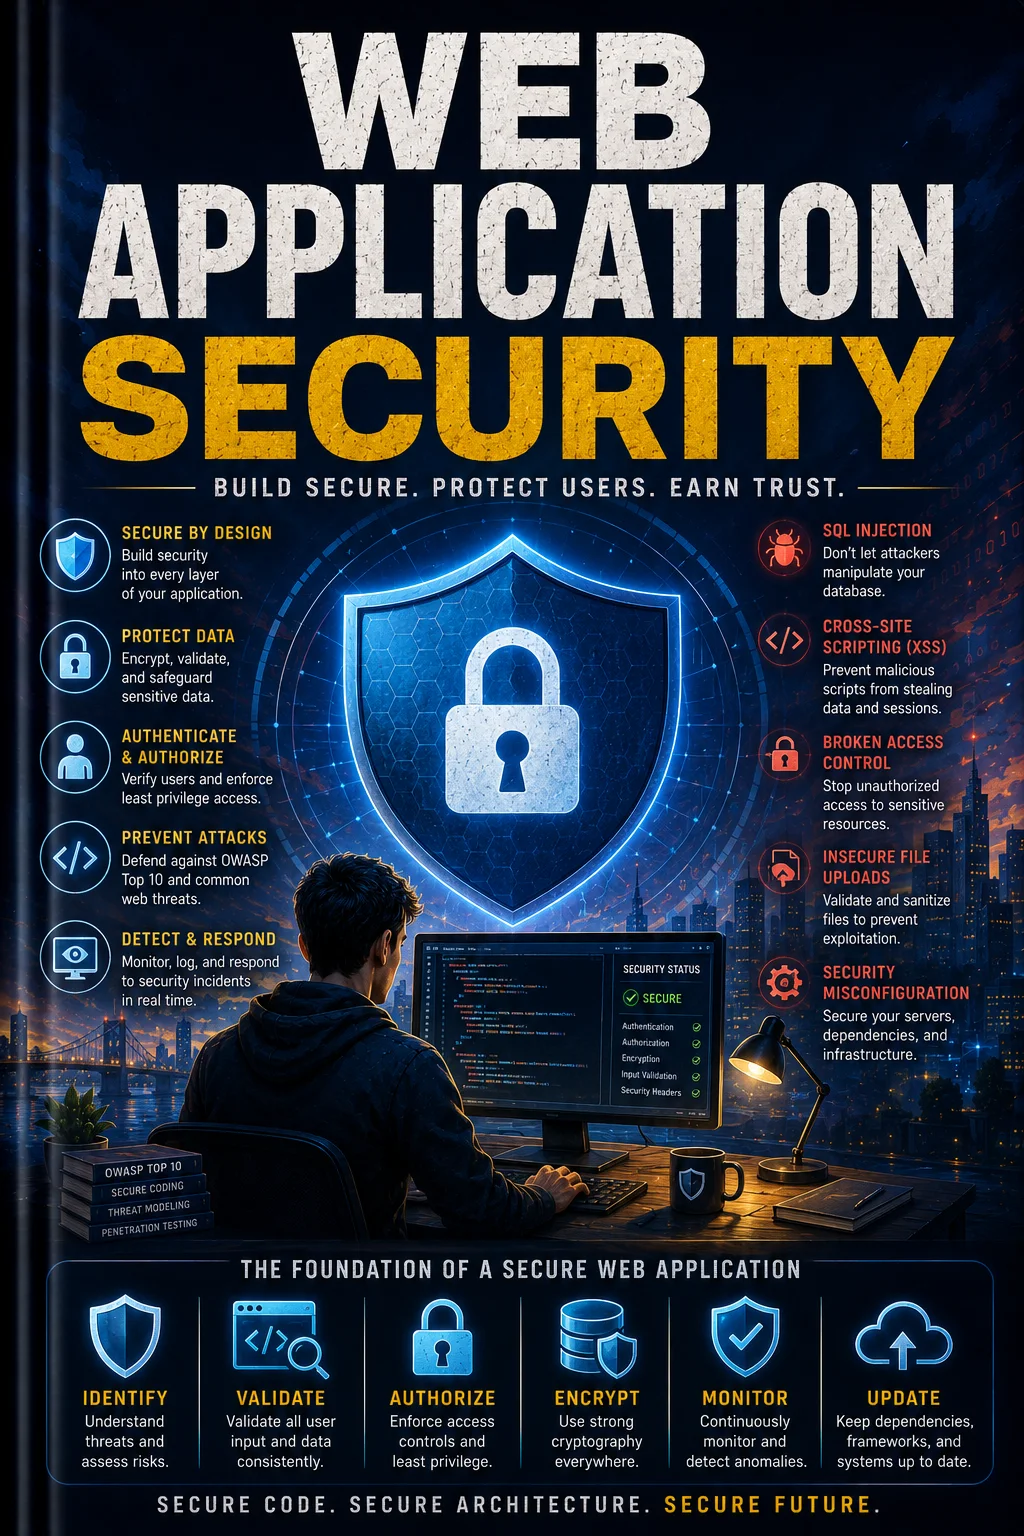
أمن تطبيقات الويب
وصول القراءة
كتاب مجاني
دليل مهني لأمن تطبيقات الويب مبني على مفاهيم OWASP، والممارسات التطويرية الآمنة، ومخاطر واجهات API، واختبار الأمان، ودمج الأمان في التشغيل والإنتاج.
المستوى: advancedاللغة: AR العربيةالتقييم: 0المراجعات: 0
كتاب
Book contents
01Chapter 1: Introduction To Web Application Security02Chapter 2: Web Architecture And Attack Surface03Chapter 2: Web Architecture Attack Surface04Chapter 3: Threat Modeling05Chapter 4: Broken Access Control06Chapter 5: Cryptographic Failures07Chapter 6: Injection Attacks08Chapter 7: Insecure Design09Chapter 8: Security Misconfiguration10Chapter 9: Vulnerable And Outdated Components11Chapter 10: Identification And Authentication Failures12Chapter 11: Software And Data Integrity Failures13Chapter 12: Security Logging And Monitoring Failures14Chapter 13: Server Side Request Forgery Ssrf15Chapter 14: Cross Site Scripting Xss16Chapter 15: Cross Site Request Forgery Csrf17Chapter 16: Clickjacking18Chapter 17: File Upload Vulnerabilities19Chapter 18: Api Security Risks20Chapter 19: Secure Coding Standards21Chapter 20: Authentication Authorization Design22Chapter 21: Secure Session Management23Chapter 22: Data Protection Privacy24Chapter 23: Security Testing Methodologies25Chapter 24: Penetration Testing Workflow26Chapter 25: Using Owasp Zap27Chapter 26: Using Burp Suite28Chapter 27: Integrating Security Into Ci Cd29Chapter 28: Container Cloud Security30Chapter 29: Monitoring Logging And Incident Response31Chapter 30: Famous Web Security Breaches32Chapter 31: Bug Bounty Hunting33Appendix E: Deeper Practice and Extra Examples
المراجعات
لا توجد مراجعات معتمدة بعد.
كتب مختارة
النقاش
0 تعليقاتلا توجد تعليقات معتمدة بعد. قد تنتظر الردود الجديدة المراجعة.