كتاب مجاني
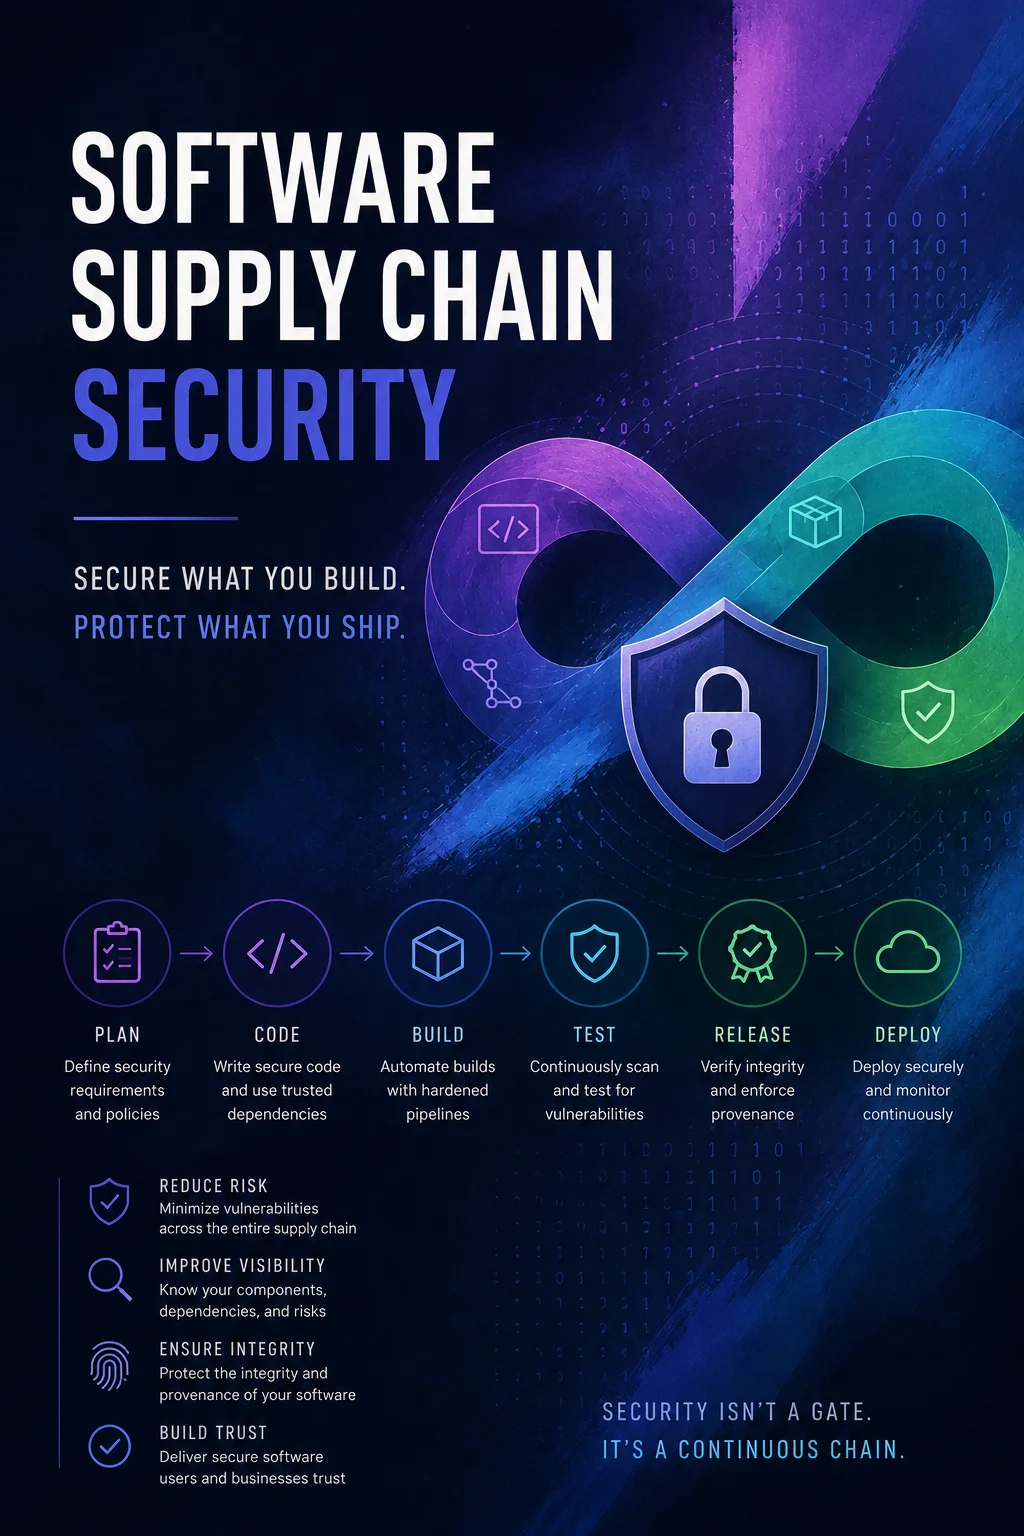
أمن سلسلة توريد البرمجيات
وصول القراءة
كتاب مجاني
كتاب أمان سلسلة توريد برمجيات حديث يغطي مخاطر التبعية، وSBOMs، والمصدر، والتحف الموقعة، ومفاهيم SLSA، وتقوية CI/CD، والأسرار، وسجلات الحزم، وسلامة الإصدار.
المستوى: advancedاللغة: AR العربيةالتقييم: 0المراجعات: 0
كتاب
Book contents
01Chapter 1: How Software Supply Chains Are Attacked02Chapter 2: Dependencies, Registries, and Package Trust03Chapter 3: Build Systems, CI Runners, and Release Risk04Chapter 4: Threat Modeling the Delivery Pipeline05Chapter 5: Lockfiles, Pinning, and Dependency Review06Chapter 6: SBOMs and Vulnerability Management07Chapter 7: Artifact Signing and Provenance08Chapter 8: Secrets Management in CI/CD09Chapter 9: SLSA Concepts and Practical Adoption10Chapter 10: Container Image Security and Scanning11Chapter 11: Policy Gates and Release Approvals12Chapter 12: Incident Response for Compromised Dependencies13Chapter 13: Harden a Node.js Release Pipeline14Chapter 14: Add SBOM and Artifact Signing15Chapter 15: Create a Dependency Upgrade Workflow16Chapter 16: Build a Supply Chain Security Checklist17Appendix E: Deeper Practice and Extra Examples
المراجعات
لا توجد مراجعات معتمدة بعد.
كتب مختارة
النقاش
0 تعليقاتلا توجد تعليقات معتمدة بعد. قد تنتظر الردود الجديدة المراجعة.