كتاب مجاني
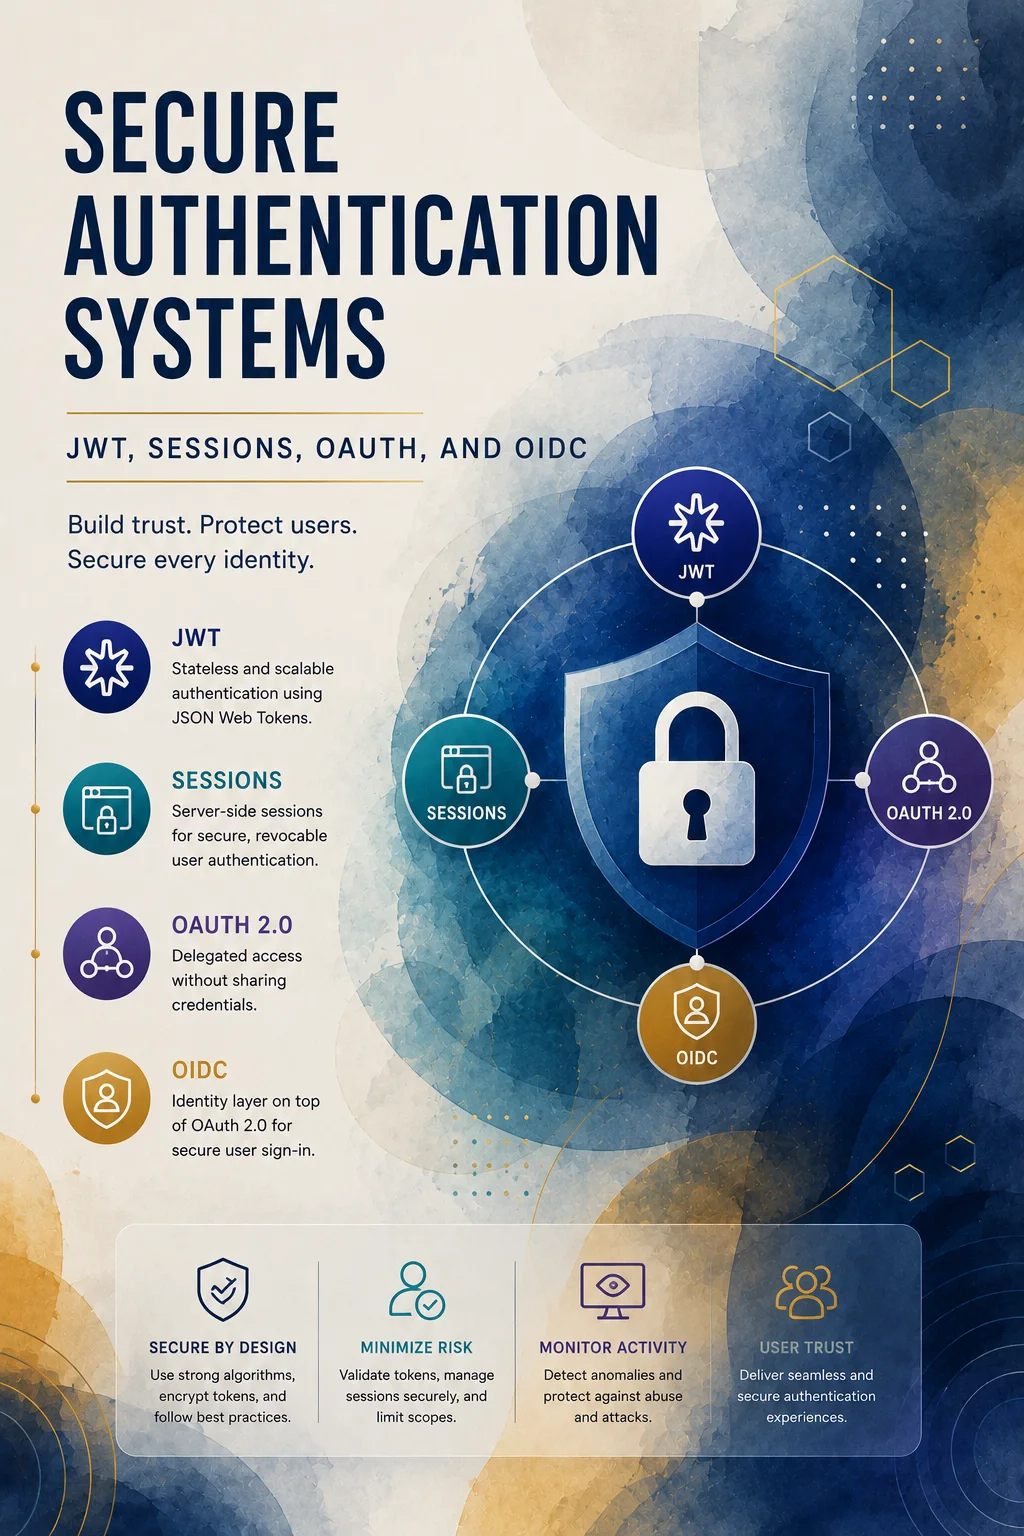
أنظمة المصادقة الآمنة: JWT والجلسات وOAuth وOIDC
وصول القراءة
كتاب مجاني
كتاب عملي يشرح تصميم وتنفيذ أنظمة مصادقة حديثة وآمنة، ويغطي كلمات المرور والجلسات وJWT وrefresh tokens وOAuth 2.0 وOpenID Connect وPKCE وMFA والضوابط التشغيلية في الإنتاج. ابدأ بالأساسيات إذا كنت تريد تثبيت مفاهيم الهوية والمصادقة والجلسات وJWT. بعد ذلك انتقل إلى أنظمة التوكن والتخزين الآمن، ثم إلى OAuth وOIDC، ثم إلى MFA والحوادث والمعمارية الكاملة. الملحقات مناسبة للمراجعة السريعة أثناء التنفيذ أو التحقيق أو التصميم.
المستوى: intermediateاللغة: AR العربيةالتقييم: 0المراجعات: 0
كتاب
Book contents
01Chapter 1: Introduction to Authentication, Authorization, and Identity02Chapter 2: Passwords, Hashing, Registration, and Login Flows03Chapter 3: Sessions, Cookies, CSRF, and Browser Security04Chapter 4: JWT Basics, Claims, Signatures, and Token Lifecycles05Chapter 5: Access Tokens, Refresh Tokens, and Rotation Strategy06Chapter 6: Revocation, Logout, Device Management, and Risk Controls07Chapter 7: API Authentication, Bearer Tokens, and Service Boundaries08Chapter 8: Secure Auth Storage for Web, Mobile, and SPA Clients09Chapter 9: OAuth 2.0 Roles, Grants, and Trust Boundaries10Chapter 10: Authorization Code Flow, PKCE, and Modern Client Guidance11Chapter 11: OpenID Connect, Identity Tokens, and UserInfo12Chapter 12: Federation, Social Login, Scopes, and Consent Design13Chapter 13: MFA, Recovery Flows, and Step-Up Authentication14Chapter 14: Threat Modeling, Monitoring, and Auth Incident Response15Chapter 15: Designing a Complete Authentication Architecture16Chapter 16: Capstone: Build and Review a Secure Auth System17Appendix A: Commands and Workflow Cheat Sheet18Appendix B: Reference Architectures and Patterns19Appendix C: Common Mistakes and Fixes20Appendix D: Best Practices Summary
المراجعات
لا توجد مراجعات معتمدة بعد.
كتب مختارة
النقاش
0 تعليقاتلا توجد تعليقات معتمدة بعد. قد تنتظر الردود الجديدة المراجعة.